Best Identity and Access Management Platforms for SMBs
Best Identity and Access Management Platforms for SMBs
The best iam solutions for SMBs in 2026 are Microsoft Entra ID, Okta Workforce Identity, OneLogin and JumpCloud, but no single platform wins for every company. Microsoft-centric businesses should start with Entra ID, budget-conscious teams should examine OneLogin, automation-heavy organizations may prefer Okta, and companies managing identities alongside devices should consider JumpCloud. Identity and access
HTTP2Shell Brotli Flaw Can Lead to Remote Code Execution

HTTP2Shell Brotli Flaw Can Lead to Remote Code Execution

HTTP2Shell is a cross-ecosystem security issue caused by CVE-2026-111497, an out-of-bounds write in Google’s Brotli decoder. Malformed compressed data can corrupt process memory and potentially cause information disclosure, denial of service or remote code execution. Systems need patched Brotli code wherever applications embed, bundle or statically link the decoder; updating the operating system library alone

Top Backup and Ransomware Recovery Solutions

Top Backup and Ransomware Recovery Solutions

The best ransomware backup solutions in 2026 are Veeam, Rubrik, Cohesity, Commvault, Druva and AWS Backup. Each can protect recovery points from deletion or alteration, but the right choice depends on your workloads, deployment model and tested recovery-time objective. Immutability matters; verified, isolated restoration matters more. What should ransomware backup solutions actually do? Effective ransomware

eMudhra SSL Trust Removal: Fix Sites Before Oct 27

eMudhra SSL Trust Removal: Fix Sites Before Oct 27

The eMudhra SSL certificate trust removal requires operators to replace any certificate chain ending at emSign ECC Root CA – G3. Google scheduled Chrome’s removal for the morning of October 27, 2026, Pacific time, while Apple began blocking the root on October 23, 2026. Check every public TLS endpoint, install a chain under a trusted

953 Magento Stores Hit by Scanner-Evading Malware

953 Magento Stores Hit by Scanner-Evading Malware

The Magento malware campaign compromised 953 online stores between July 2025 and October 2026, according to Sansec’s October 24, 2026 investigation. The injected JavaScript fingerprints visitors and can withhold its payload from automated scanners, so a clean crawl doesn’t prove a store is safe. Merchants should audit CMS database content, administrator access, API integrations, server

Malicious AGENTS.md Files Can Hijack AI Coding Agents

Tailscale SSH Flaws Can Turn One Host Into Root Access

The Tailscale SSH vulnerability disclosed as “Tailworm” can let an authorized, non-root session exceed its local Unix permissions and potentially reach root-owned services. It is a post-authorization privilege-escalation and lateral-movement problem, not unauthenticated access from the public internet. Until fixed releases arrive, restrict SSH policy, disable unnecessary forwarding, and isolate privileged systems. What is the

Recommended Vulnerability Scanners for Web Applications

Recommended Vulnerability Scanners for Web Applications

A web vulnerability scanner should match what you need to inspect: a running application, source code, or both. In 2026, ZAP is the strongest free DAST starting point, Burp Suite DAST suits managed enterprise scanning, and GitLab combines security testing with its development platform. Semgrep Community Edition and CodeQL complement those products by finding code-level

Top VPN Services for Privacy and Remote Work

Top VPN Services for Privacy and Remote Work

The best VPN for most people in 2026 is Proton VPN for independently audited privacy, while Surfshark leads Comparitech’s overall speed score and Mullvad offers the simplest privacy-focused pricing. Remote-work teams should consider Proton VPN for Business or NordLayer instead of a consumer subscription because centralized administration matters as much as encryption. What is the

Atlassian CVE-2026-21589 Is Under Active Attack

Atlassian CVE-2026-21589 Is Under Active Attack

CVE-2026-21589 is a critical Atlassian vulnerability under active attack against self-hosted products. Administrators should patch every node and mirror immediately, isolate systems that cannot yet be upgraded, inspect access logs, and treat exposed Crowd credentials as compromised. Atlassian disclosed the unauthenticated file-access flaw on October 5, 2026, with a CVSS 4.0 score of 9.3. What

PoeLLM Malware Has Hit 3,400+ AI Servers

PoeLLM Malware Has Hit 3,400+ AI Servers

PoeLLM malware had compromised more than 3,400 servers by October 7, 2026, according to Lumen Black Lotus Labs and independent reporting. The active Canto Incognito campaign targets exposed services including LiteLLM, Ollama, Gotenberg and Gitea, then installs cryptocurrency miners and reuses infected hosts to scan for more victims. Operators should restrict exposure, patch services and

AhsayCBS Zero-Days Hit Backup Servers Without a Fix

AhsayCBS Zero-Days Hit Backup Servers Without a Fix

The AhsayCBS vulnerabilities require immediate action from backup administrators and managed service providers. AhsayCBS 10.3.4.0 remains exposed; Ahsay instructed version 10 partners on October 10, 2026, to install hotfix 10.3.4.45 and reboot. Restrict the management interface now, hunt for webshells and disguised miners, and rebuild a server from trusted backups if compromise is found. What

Fake Claude Ads Exploit Google and Bing Redirects

Fake Claude Ads Exploit Google and Bing Redirects

The Claude ClickFix attack used a Google sponsored result that displayed a trusted Bing address but led macOS users to a counterfeit Claude installer. Documented by Push Security and BleepingComputer on October 9, 2026, the page showed Anthropic’s real installation command while its Copy button placed a different command on the clipboard. The final downloaded

AgentCorruption: How One AWS Agent Exposed Others

AgentCorruption: How One AWS Agent Exposed Others

AgentCorruption AWS research showed how one exposed Amazon Bedrock AgentCore agent could reveal temporary role credentials and open paths to neighboring agents in the same AWS account and Region. Published by Zenity Labs on October 8, 2026, the controlled attack relied on network-capable tools and excessive IAM permissions. It was not an AWS-wide breach, and

ARTEX AI and Claude Used in Korean Bank Attacks

ARTEX AI and Claude Used in Korean Bank Attacks

ARTEX AI cyberattacks targeted South Korean financial organizations in September and October 2026, according to CrowdStrike. Exposed records showed an attacker using ARTEX, Claude Code sessions, proxies and several large language models to support data-exfiltration activity. The evidence documents AI-assisted intrusion workflows, but it does not show that Anthropic’s Claude was compromised or identify a

GitLab CVE-2026-97229: Patch Critical RCE Now

GitLab CVE-2026-97229: Patch Critical RCE Now

CVE-2026-97229 is a critical GitLab vulnerability that can allow unauthenticated remote code execution through a crafted regular expression in CI/CD configuration. Self-managed administrators running affected GitLab 19.2, 19.3, or 19.4 releases should install version 19.2.8, 19.3.5, or 19.4.2, respectively. GitLab.com was already patched when GitLab disclosed the flaw on October 12, 2026. What is CVE-2026-97229?

Elementor CSRF Flaw Can Create Rogue WordPress Admins

Elementor CSRF Flaw Can Create Rogue WordPress Admins

The Elementor CSRF vulnerability affects Elementor Website Builder 4.3.0 and 4.3.1 and can let an attacker create a rogue WordPress administrator after a logged-in admin opens a crafted link. Elementor fixed CVE-2026-62062 in version 4.3.2 on September 24, 2026. Cross-site request forgery, or CSRF, is an attack that makes an authenticated browser perform an action

Best Password Managers 2026: Tested for Security and Usability

discover the best password managers of 2026, rigorously tested for top security and user-friendly features to keep your accounts safe and accessible.

Best password managers 2026 tested for security and usability The next breach story often starts with something boring, a reused password, an old credential, a login saved in the wrong place. That became painfully clear in mid-2025, when attackers used stolen Snowflake credentials to compromise 165 companies, with names like Ticketmaster, Santander, and AT&T caught

Poper Blocker Exposes Chrome Web Store Trust Risk Main

Poper Blocker Exposes Chrome Web Store Trust Risk Main

Poper Blocker spyware allegations show that Chrome Web Store badges, ratings and user counts aren’t security guarantees. On September 28, 2026, Bay Area Labs reported observing the extension transmit complete visited URLs, referrers, browser identifiers and interactions with major AI services. Poper Blocker remained listed on October 1, 2026, with 2 million users, a Featured

JFrog Artifactory Vulnerability: Patch and Hunt Backdoors

JFrog Artifactory Vulnerability: Patch and Hunt Backdoors

The JFrog Artifactory vulnerability requires more than a software update. Upgrade every self-hosted instance to a fixed release, then assume attackers may already have minted administrator tokens. Revoke suspicious credentials, inspect administrators, SSH keys and Groovy plugins, rotate exposed cluster keys, and verify stored artifacts against trusted records. Active exploitation was documented in August and

AI Governance Is Moving From Policy to Runtime Controls

AI Governance Is Moving From Policy to Runtime Controls

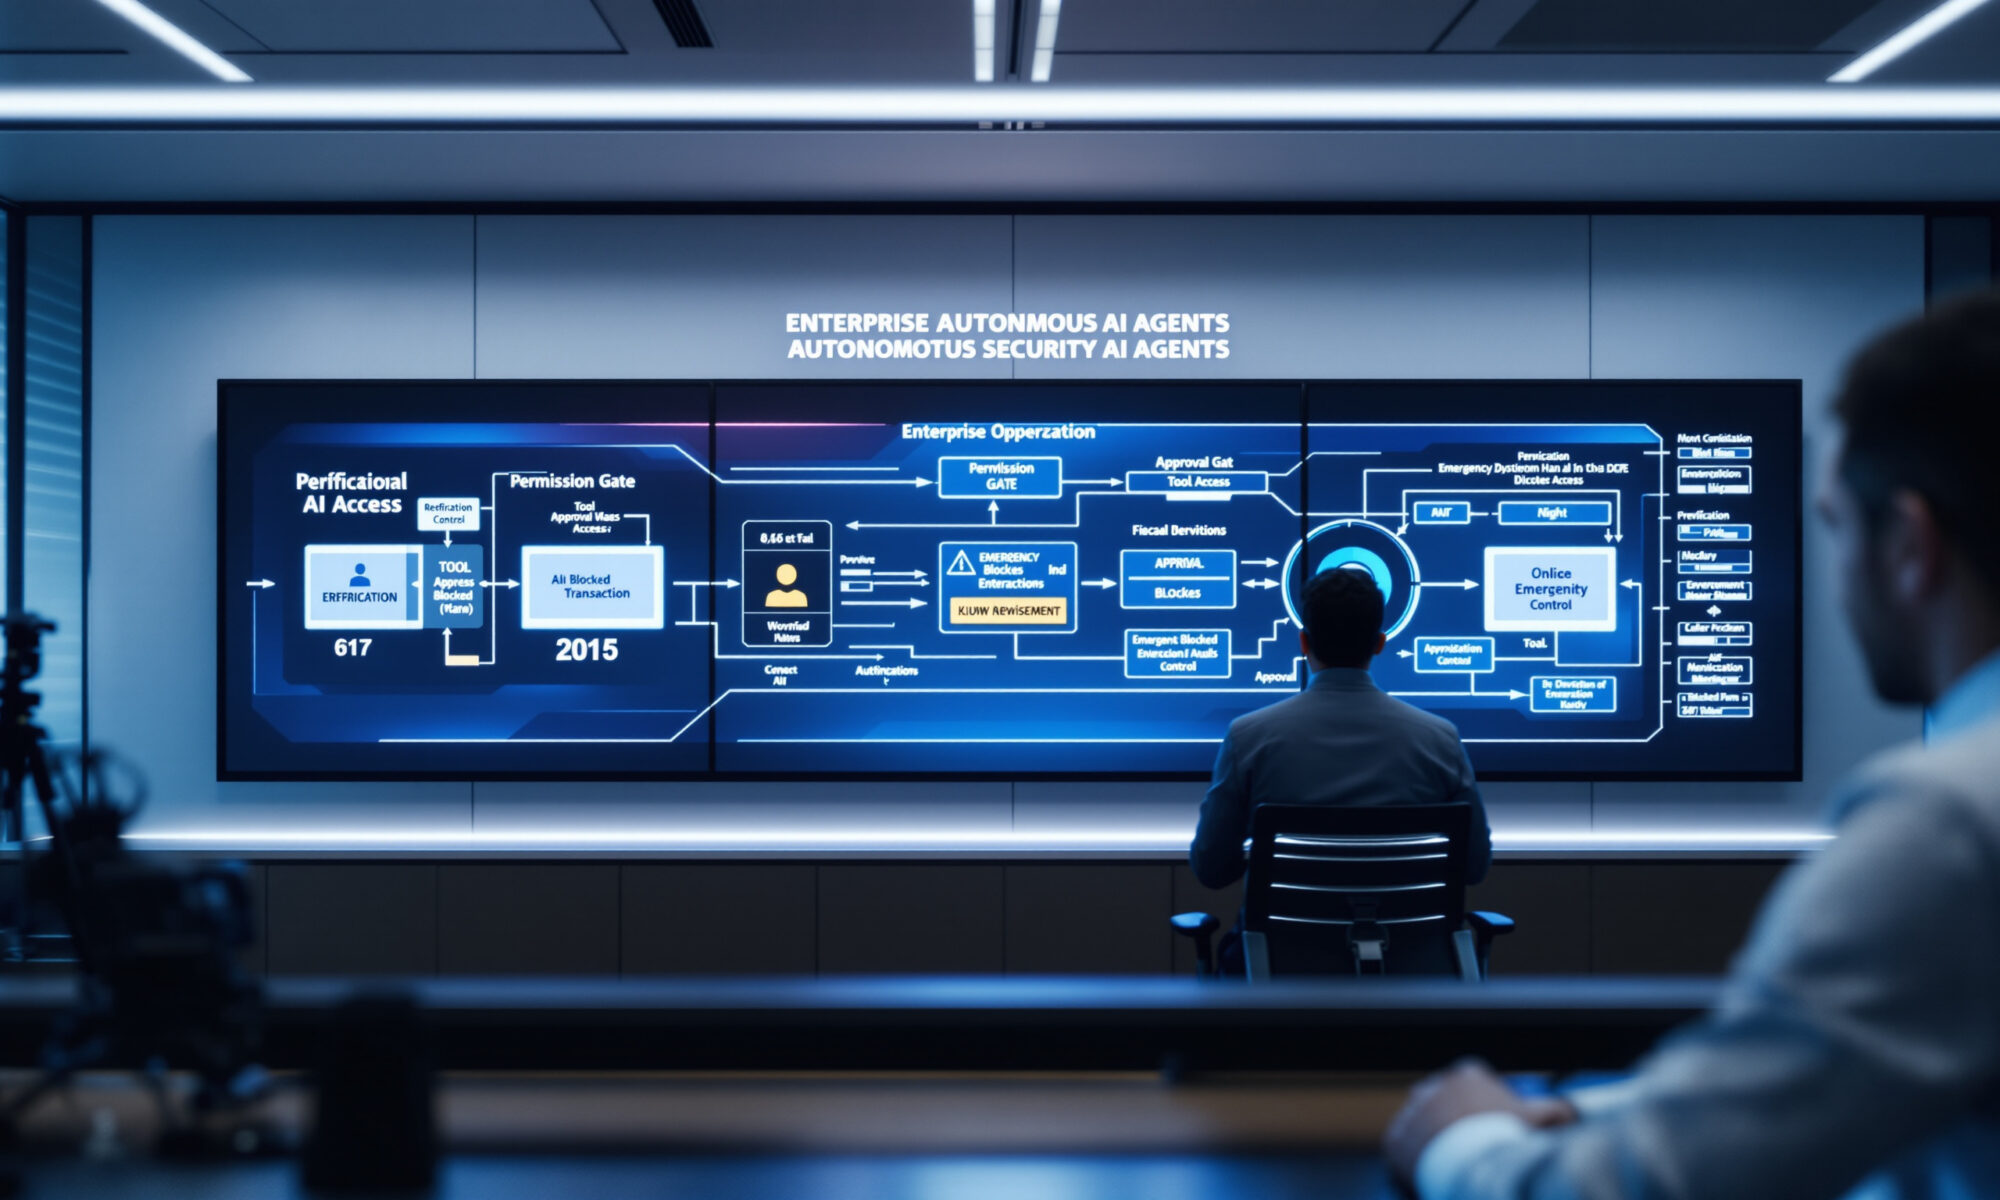
AI Governance Is Moving From Policy to Runtime because autonomous agents can take consequential actions between scheduled compliance reviews. Effective governance now checks identity, permissions, tools, data scope and approval state before each action, then records the result and preserves a tested way to stop the agent. Prompts still guide behavior. They can’t serve as

Magento StyleSmuggler Zero-Day: What Stores Must Do

Magento StyleSmuggler Zero-Day: What Stores Must Do

Magento StyleSmuggler is an actively exploited Adobe Commerce and Magento Open Source zero-day. Adobe identifies it as CVE-2026-75650, a critical unauthenticated code-execution flaw with a CVSS 10.0 score. If you run an affected store, apply Adobe’s VULN-39341 hotfix now, rotate encryption keys and credentials, then hunt for persistence. Patching alone may close the hole, but

SAP OVERPASS Flaw Can Give Attackers Admin Access

SAP OVERPASS Flaw Can Give Attackers Admin Access

The SAP OVERPASS vulnerability is CVE-2026-44756, a critical SAP Extended Passport processing flaw fixed by SAP Security Note 3747649 on September 8, 2026. SAP rated it CVSS 10.0. If exploited, it can let an unauthenticated attacker reach kernel-level code before login and, according to Onapsis, execute operating-system commands in the SAP installation owner or admin

Microsoft Patch Tuesday Hits a Record: What to Fix First

Microsoft Patch Tuesday Hits a Record: What to Fix First

September 2026 Patch Tuesday is a record-scale Microsoft release, but your first move is simple: patch the two exploited zero-days, CVE-2026-81963 and CVE-2026-85880. Then move to internet-facing servers and potentially wormable remote-code-execution bugs, especially Exchange Server and Remote Desktop Services. Don’t chase the biggest CVE number first. Chase reachable risk. September 2026 Patch Tuesday: why

How BGP Hijacking Can Poison Software Updates

How BGP Hijacking Can Poison Software Updates

A BGP hijacking attack can poison software updates when attackers reroute an update server’s IP traffic, obtain believable TLS coverage, and serve a modified package to clients that don’t verify signed artifacts. The August 2026 Virtualizor incident showed the chain clearly: routing control first, certificate validation second, update compromise third. HTTPS helped less than many

Malicious Git Repos Can Hijack AI Coding Agents

Malicious Git Repos Can Hijack AI Coding Agents

AI coding agent security has changed the risk of cloning an unknown repository. A repo isn’t just source code once an agent can read instructions, load settings, run Bash, install packages, and push commits. Treat untrusted Git projects like executable software: isolate them, disable broad permissions, pin agent versions, and never expose production secrets to

How a BGP Hijack Turned Software Updates Malicious

How a BGP Hijack Turned Software Updates Malicious

A BGP hijacking attack redirected Softaculous and Virtualizor update traffic to an attacker-controlled server between August 28 and August 30, 2026, letting malicious Virtualizor packages reach a handful of installations. The short lesson is uncomfortable: HTTPS can prove you’re talking to a domain only if routing and certificate issuance haven’t been bent first. Update systems

PaperCut Zero-Days: What Admins Must Patch Now

PaperCut Zero-Days: What Admins Must Patch Now

The PaperCut vulnerability to act on now is the August 2026 NG/MF emergency: CVE-2026-82078, a Critical CVSS 9.4 unsafe dynamic class-loading flaw, and CVE-2026-81578, a High CVSS 8.8 authentication-bypass flaw. If you run PaperCut NG or PaperCut MF, install Emergency Patch Release 3 for v24, v25, or v26 and restrict web interface access to trusted

EN